Others
Begineer Friendly
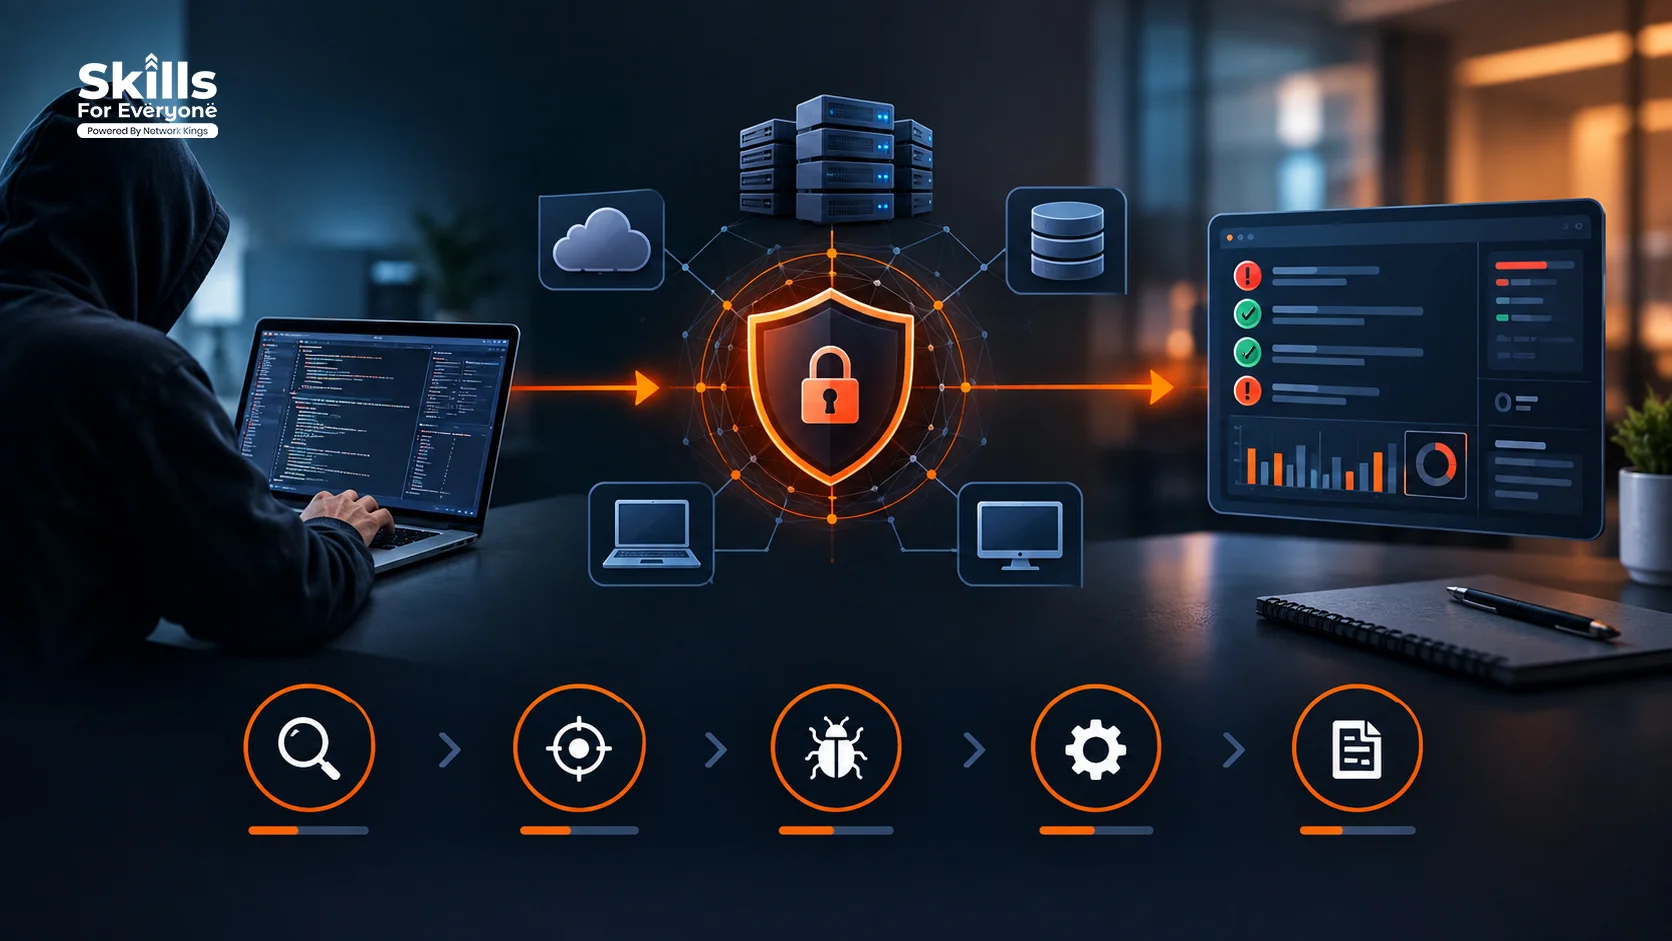
Penetration testing is a controlled, authorized security exercise in which a skilled tester simulates real attack techniques against a network, application, or system to find exploitable weaknesses before criminals do. It goes beyond scanning for known flaws by actually attempting to exploit them, showing exactly how far an attacker could get and what damage they could cause.
For businesses, this distinction matters. A vulnerability scan tells you a door might be unlocked. A penetration test tells you whether someone can actually walk through it, what they can reach once inside, and how much of your business is exposed as a result.
What Penetration Testing Means for Businesses
Most organizations assume their firewalls, access controls, and security software are working as intended. Penetration testing exists to challenge that assumption. Rather than trusting that security controls function correctly, a pen test actively probes them the way a real attacker would, using the same reconnaissance methods, exploitation techniques, and persistence tactics seen in actual breaches.
This gives decision-makers something far more useful than a checklist. It gives them evidence. A report showing that a tester moved from a low-privilege employee account to full administrative access over a weekend carries more weight internally than any theoretical risk assessment.
How Penetration Testing Works
A professional penetration test typically follows a structured methodology, even though the specific tools and techniques vary by engagement.
Reconnaissance and Scoping
The tester first defines the scope with the client, agreeing on which systems, applications, or networks are in bounds. They then gather information about the target, including exposed services, domain infrastructure, employee details, and publicly available technical footprints.
Vulnerability Discovery
Using both automated tools and manual analysis, the tester identifies potential weaknesses across the attack surface, such as outdated software, misconfigured services, weak authentication, or insecure coding patterns.
Exploitation
This is where penetration testing separates itself from vulnerability assessment. The tester attempts to actively exploit discovered weaknesses to confirm they are real and usable, not just theoretical.
Post-Exploitation
If exploitation succeeds, the tester evaluates what further access or data exposure it enables, such as lateral movement across the network or access to sensitive customer records.
Reporting and Remediation Guidance
The engagement ends with a detailed report outlining what was found, how it was exploited, the business risk involved, and recommended remediation steps.
Types of Penetration Testing
Penetration testing is not one-size-fits-all. Different environments and business needs call for different testing approaches.
Type | What It Tests | Typical Focus | Common Use |
Network penetration testing | Internal and external network infrastructure | Firewalls, servers, routers, exposed services | Identifying unauthorized access points into core systems |
Web application penetration testing | Websites and web-based platforms | Authentication, input handling, session management | Protecting customer-facing applications and portals |
API penetration testing | Application programming interfaces | Authorization logic, data exposure, endpoint security | Securing integrations between systems and services |
Cloud penetration testing | Cloud infrastructure and configurations | Identity permissions, storage settings, misconfigurations | Assessing risk in cloud-hosted environments |
Internal penetration testing | Systems accessible from inside the network | Insider threat scenarios, lateral movement | Simulating a compromised employee device or account |
External penetration testing | Internet-facing systems | Perimeter defenses, public entry points | Simulating an outside attacker with no prior access |
Testing engagements are also categorized by how much information the tester is given beforehand. Black-box testing means the tester starts with little to no internal knowledge, closely mirroring an outside attacker. White-box testing provides full access to source code, architecture, and credentials, allowing deeper analysis. Gray-box testing sits between the two, giving the tester partial knowledge, similar to what a lower-privilege insider might have.
Penetration Testing Versus Vulnerability Assessment
These two terms are often used interchangeably, which creates confusion for businesses trying to choose the right service.
A vulnerability assessment identifies and catalogs potential weaknesses, usually through automated scanning, and ranks them by severity. It answers the question of what might be wrong.
A penetration test goes further by attempting to exploit those weaknesses under real conditions. It answers the question of what an attacker could actually do if the weakness were left unaddressed. Vulnerability assessments are broader and more frequent, while penetration tests are deeper and more targeted.
What a Penetration Test Can Uncover
A well-scoped test can expose weaknesses that may otherwise remain difficult to identify. Depending on the environment, these can include:
Weak authentication or password controls
Improper authorization and excessive privileges
Vulnerable network services
Web application security flaws
API access control weaknesses
Cloud configuration errors
Insecure data exposure
Poorly protected administrative interfaces
Opportunities for privilege escalation or lateral movement
The value is not simply finding vulnerabilities. A skilled tester can help demonstrate how weaknesses relate to one another and whether an attacker could move from an initial foothold toward sensitive systems or information.
Why Businesses Need Penetration Testing
Modern organizations often depend on interconnected networks, cloud platforms, SaaS applications, APIs, remote access systems, and third-party services. This creates an expanding attack surface that can be difficult to evaluate using automated security tools alone.
Penetration testing gives businesses an attacker-focused perspective. It can help organizations:
Validate whether important security controls work as intended
Identify exploitable weaknesses before they are abused
Understand realistic attack paths
Prioritize remediation based on potential impact
Test the security of newly deployed systems
Support security and compliance requirements where applicable
It can also provide useful evidence for security teams, technology leaders, and stakeholders who need to understand how technical weaknesses could translate into business risk.
When Businesses Should Conduct a Penetration Test
Many organizations test annually as a baseline, but certain events call for additional testing outside that schedule. These include major infrastructure changes, new application deployments, mergers or acquisitions that introduce unfamiliar systems, and after any security incident to confirm remediation was effective.
What Happens After a Penetration Test
The value of a penetration test depends heavily on what happens afterward. The report should be reviewed with technical and business stakeholders, findings should be prioritized by actual risk rather than alphabetical order, and remediation should be verified through retesting rather than assumed complete once a fix is deployed.
Conclusion
Penetration testing gives businesses something automated tools alone cannot, which is proof of how their defenses hold up against real attack behavior. By combining reconnaissance, exploitation, and clear reporting, it turns abstract security risk into concrete, actionable priorities that organizations can address before an actual attacker gets the chance.
Frequently Asked Questions (FAQs)
1. How is penetration testing different from vulnerability scanning?
Vulnerability scanning primarily uses automated tools to identify potential security weaknesses, while penetration testing goes further by manually validating selected vulnerabilities through controlled exploitation. A penetration test can also show how multiple weaknesses could be chained together to create a realistic attack path.
2. Can penetration testing identify vulnerabilities that automated scanners miss?
Yes. Automated scanners are useful for identifying known vulnerabilities and configuration issues, but they may not understand complex business logic, authorization flaws, chained vulnerabilities, or application-specific attack paths. Manual testing can uncover weaknesses that depend on how different components interact.
3. What is the difference between black-box, white-box, and gray-box penetration testing?
The difference is the amount of information provided to the tester. Black-box testing provides little or no internal information and simulates an external attacker. White-box testing provides extensive technical information, such as source code or architecture details. Gray-box testing provides partial knowledge and represents scenarios such as a user with limited access.
4. Can penetration testing test cloud environments?
Yes. Cloud penetration testing can assess areas such as identity and access management, exposed services, storage permissions, network configurations, and application interfaces. However, the scope must account for the cloud provider's policies and the customer's responsibilities within the shared responsibility model.
5. What happens if a penetration tester gains administrative access?
The tester normally documents and safely validates the level of access and potential impact according to the agreed rules of engagement. They may investigate whether administrative privileges allow access to additional systems or sensitive resources, but destructive actions or unnecessary data access should be avoided unless explicitly authorized.
6. How often should businesses perform penetration testing?
There is no single testing schedule that applies to every organization. Frequency depends on factors such as business risk, regulatory requirements, infrastructure changes, application releases, and exposure to the internet. Additional testing may be appropriate after major architectural changes, significant application updates, mergers, acquisitions, or security incidents.
7. Does penetration testing guarantee that a business is secure?
No. A penetration test provides a point-in-time assessment of the systems and attack scenarios included within its scope. New vulnerabilities, configuration changes, software updates, and emerging attack techniques can introduce additional risks. Penetration testing should therefore complement vulnerability management, security monitoring, secure development, and other cybersecurity controls.